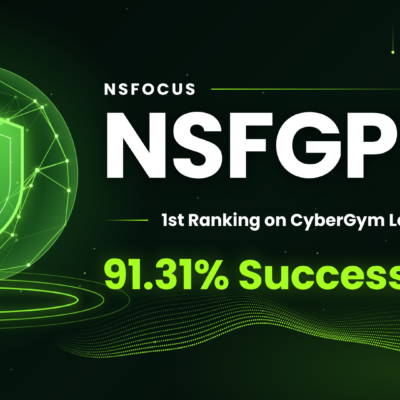
First Ranking! NSFOCUS Tops Globally on CyberGym Leaderboard Again

NSFOCUS NSFGPT Foundation Model (SecLLM-3.6-27B) just ranked first again globally on the CyberGym Model-Focused Leaderboard with a task success rate of 91.31%! This is a pure model leaderboard. Under CyberGym’s Model-Focused rules, models are evaluated strictly using a generic harness—without fixed stages, external tools, knowledge bases, or specialized agentic designs—purely...
Apache HTTP Server Remote Code Execution Vulnerability (CVE-2026-119618) Advisory

Overview NSFOCUS CERT recently noted that Apache had released a security advisory announcing a fix for a remote code execution vulnerability (CVE-2026-119618) in Apache HTTP Server. Due to improper synchronization when accessing shared resources in the assign_headers() function of Apache HTTP Server's mod_http2 module, an unauthenticated attacker could trigger a...

OpenSSH/musl Password Authentication Bypass Vulnerability (CVE-2026-123158) Advisory

Overview Recently, NSFOCUS CERT monitored that OpenSSH released a security update fixing the OpenSSH/musl password authentication bypass vulnerability (CVE-2026-123158). Because crypt() in musl libc returns "*" upon failure, when the target account's password field is "*" and other accounts using password hashes exist on the system while SSH password authentication...

Adversarial | Intelligent | Evolving: How NSFOCUS Smart Security 4.0 Redefines its Security Paradigm in the AI Era

SANTA CLARA, Calif., November 11, 2026 – NSFOCUS recently launched its Smart Security 4.0 strategy during the 2026 TechWorld Smart Security Conference held in Beijing, which seeks to rebuild security capabilities around an intelligence-native foundation, continuously evolve to counter emerging threats, improve operational efficiency through autonomous operations, and strengthen security and resilience...

Linux Kernel IPv4 TCP Use-After-Free Vulnerability (CVE-2026-98432) Advisory

Overview Recently, NSFOCUS CERT monitored that Linux released a security update to fix the Linux Kernel IPv4 TCP use-after-free vulnerability (CVE-2026-98432). Due to a race condition issue in the Linux kernel IPv4 network subsystem when concurrently handling TCP connection requests or socket migration, an unauthenticated attacker can trigger a use-after-free...

NSFOCUS
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.