Blog

Millions of Devices May Be Affected, and Yeskit Botnet Family Spreads on a Massive Scale by Exploiting F5 BIG-IP Vulnerability

Background   On May 4, 2022, F5 issued a security bulletin regarding a remote code execution vulnerability in iControlREST component of BIG-IP products. The CVE number of the vulnerability is CVE-2022-1388. The vulnerability can bypass authentication and remotely execute arbitrary code with a vulnerability score of CVSS up to 9.8....

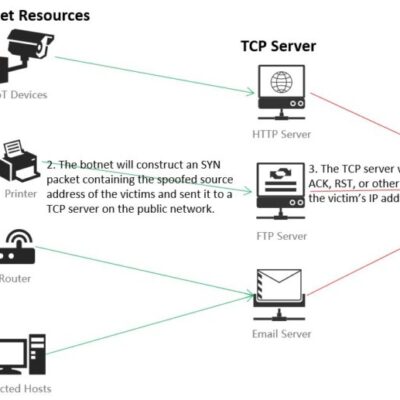
Research and Analysis of Middlebox-based TCP Reflective Amplification Attacks

Abstract In August 2021, Kevin Bock and his team from the University of Maryland and the University of Colorado Boulder proposed a new TCP reflective amplification attack method initiated by the middlebox at the USENIX conference. (See more details at https://geneva.cs.umd.edu/papers/usenix-weaponizing-ddos.pdf) In mid-April this year, NSFOCUS spotted that one of...

Multiple OpenSSL Security Vulnerabilities Alerts

Overview Recently, NSFOCUS CERT found that OpenSSL issued a security notice, which fixed multiple security vulnerabilities in OpenSSL products. OpenSSL is an open source software library package. Applications can use this package to communicate securely, avoid eavesdropping, and confirm the identity of the other end of the connection. It is...

NSFOCUS Managed Security Service Case: Protection Policy Tuning for Further Improved Result in a 170Gbps DDoS Incident

Incident Response On mid-2021, a multinational telecom service provider was attacked by a sudden large-scale DDoS attack with the peak value of 170Gbps with maximum 5Gbps of malicious traffic leakage, with equivalent Mitigation Effect (mitigated malicious traffic/total ingress traffic) stays at least 97%. The service provider did not encounter service...

F5 BIG-IP iControl REST Authentication Bypass Vulnerability (CVE-2022-1388) Alert

Overview Recently, NSFOCUS CERT detected that F5 issued a security bulletin to fix an authentication bypass vulnerability in BIG-IP. Unauthenticated attackers can use the control interface to exploit, through the BIG-IP management interface or its own IP address. Network access to the iControl REST interface to execute arbitrary system commands,...

NSFOCUS
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.