
Overview
Recently, NSFOCUS CERT monitored the public disclosure of PHP Remote Code Execution (RCE) vulnerabilities (CVE-2026-109618 / CVE-2026-109619).
Due to memory management flaws in PHP Core—where longjmp() handles Out-Of-Memory (OOM) errors leading to failed memory allocations, as well as various global state handling operations—a Use-After-Free (UAF) condition can occur. Unauthenticated remote attackers can trigger memory corruption by crafting specially designed multipart requests, potentially leading to process crashes or arbitrary code execution under the privileges of the PHP service account.
The CVSS score is 9.2. Vulnerability details have been publicly disclosed, and affected users are advised to perform self-examinations and implement protective measures as soon as possible.
Reference Links:
https://github.com/php/php-src/security/advisories/GHSA-w8hw-w9fx-j79w
https://github.com/php/php-src/security/advisories/GHSA-6wmf-4rv5-p3rp
Scope of Impact
Affected Versions:
- PHP <= 8.5.11
- PHP <= 8.4.26
- PHP <= 8.3.35
- 5.4 <= PHP <= 8.2.34
Note: The affected scope involves application components such as WordPress, MediaWiki, phpBB, Magento, Laravel, Symfony, and Drupal, spanning PHP 5.x to PHP 8.5. Please note that PHP 5.x, 7.x, 8.0, and 8.1 branches have reached End-of-Life (EOL).
Unaffected Versions:
- PHP >= 8.5.12
- PHP >= 8.4.27
- PHP >= 8.3.36
- PHP >= 8.2.35
Detection
Version Check
Users can check their current PHP version to determine whether their environment is affected:
| php -v |
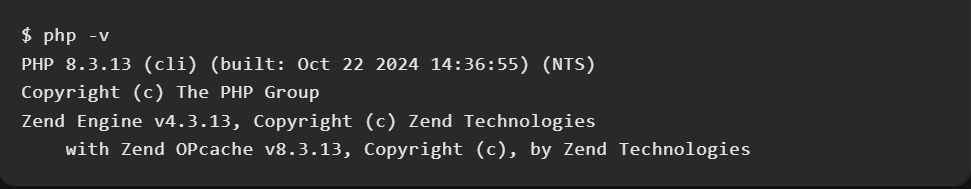
If the running version falls within the affected range, the system may be exposed to security risks.
Mitigation
Official Update
Official patches fixing these vulnerabilities have been released. Affected users should upgrade as soon as possible:
Download Link: https://github.com/php/php-src/releases
Temporary Measures
If immediate upgrading is not feasible, the following mitigation steps can be taken provided they do not impact business operations:
- Adjust Memory and Session Settings: Remove predictable single-request memory limits by setting memory_limit=-1. Disable session upload progress functionality by setting fatal_error_backtraces=0 and session.upload_progress.enabled=0, then restart PHP-FPM or the Web server.
- Enable Strict Session Mode: Set session.use_strict_mode = 1 to reduce the risk of attackers specifying arbitrary session IDs.
- Audit Affected Assets: Conduct a comprehensive inventory of all hosts and container instances running PHP 5.x through PHP 8.5. Closely monitor execution logs of Web services and PHP, focusing on anomalous worker crashes, warning/deprecation logs, cleanup-phase diagnostics, fatal errors, abnormal child process creation, or unexpected file writing behaviors.
Statement
This advisory is only used to describe a potential risk. NSFOCUS does not provide any commitment or promise on this advisory. NSFOCUS and the author will not bear any liability for any direct and/or indirect consequences and losses caused by transmitting and/or using this advisory. NSFOCUS reserves all the rights to modify and interpret this advisory. Please include this statement paragraph when reproducing or transferring this advisory. Do not modify this advisory, add/delete any information to/from it, or use this advisory for commercial purposes without permission from NSFOCUS.
About NSFOCUS
NSFOCUS, a pioneering leader in cybersecurity, is dedicated to safeguarding telecommunications, Internet service providers, hosting providers, and enterprises from sophisticated cyberattacks.
Founded in 2000, NSFOCUS operates globally with over 3000 employees at two headquarters in Beijing, China, and Santa Clara, CA, USA, and over 50 offices worldwide. It has a proven track record of protecting over 25% of the Fortune Global 500 companies, including four of the five largest banks and six of the world’s top ten telecommunications companies.
Leveraging technical prowess and innovation, NSFOCUS delivers a comprehensive suite of security solutions, including the Intelligent Security Operations Platform (ISOP) for modern SOC, DDoS Protection, Continuous Threat Exposure Management (CTEM) Service and Web Application and API Protection (WAAP). All the solutions and services are augmented by the Security Large Language Model (SecLLM), ML, patented algorithms and other cutting-edge research achievements developed by NSFOCUS.

