Cisco Policy Suite Cluster Manager Default Password Vulnerability

Cisco released an advisory on July 18 to alert users about a critical vulnerability (CVE-2018-0375) in its Cluster Manager of Cisco Policy Suite. This vulnerability could allow an unauthenticated, remote attacker to log in to an affected system using the root account, which has default, static user credentials. The vulnerability...
MODX Revolution Remote Code Execution Vulnerability

Recently MODX announced two critical vulnerabilities (CVE-2018-1000207) in MODX Revolution 2.6.4 and earlier versions.  A remote attacker could use the vulnerabilities to execute arbitrary code and further to control the website or delete files. Reference: https://forums.modx.com/thread/104040/revolution-2-6-4-and-prior-two-cricital-vulnerabilities-upgrade-mandatory-patch#dis-post-559515 Affected Versions MODX Revolution <= 2.6.4 Unaffected Versions  Modx Revolution >= 2.6.5 Solution Users are...

NSFOCUS Weekly Cybersecurity Report

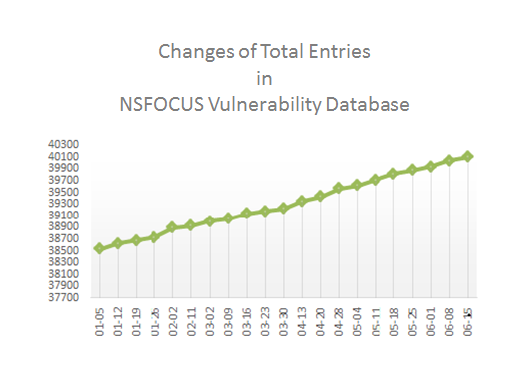
(Report ID: 201824) Internet Threat Status CVE Statistics Last week we saw a slight increase in the total entries of CVE IDs.   Threat Review New 'Lazy FP State Restore' Vulnerability Found in All Modern Intel CPUs Date: 06-13-2018 Description: Hell Yeah! Another security vulnerability has been discovered in Intel...

Drupal Remote Code Execution Vulnerability Analysis

Overview Drupal released a security advisory on 28 March 2018 to disclose a remote execution code (RCE) vulnerability in the Drupal core, sa-core-2018-002 (CVE-2018-7600). Soon, two more security advisories were also published within a month, including a Cross-Site Scripting (XSS) vulnerability and a critical code execution vulnerability — sa-core-2018-004 (CVE-2018-7602)....

2017 DDoS and Web Application Attack Landscape

1 Introduction New Internet-based technologies and models, such as cloud computing, big data, Internet of Things (IoT), and mobile computing, are profoundly influencing transformations in the cyberspace. In this context, cyber threats keep evolving and upgrading. Distributed denial-of-service (DDoS) attacks and web application attacks are the main security threats facing...

Oracle WebLogic Server RCE Deserialization Vulnerability

On 17 April, the local time in California, Oracle released its Critical Patch Update(CPU) Advisory in which a critical WebLogic deserialization vulnerability (CVE-2018-2628) allowing remote code execution without authorization was disclosed. This vulnerability was first discovered by an NSFOCUS researcher, who reported it to Oracle immediately. More information about this...

NSFOCUS
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.