Overview On July 21, 2021, NSFOCUS detected that Oracle released the April 2021 Critical Patch Update (CPU), which fixed 342 vulnerabilities of varying risk levels. Among these vulnerabilities, three severe ones are easy to exploit to affect WebLogic. Users are advised to take measures without delay to protect against the...

Category: Emergency Response
Oracle July 2021 Critical Patch Update for All Product Families
Overview On July 21, 2021, NSFOCUS detected that Oracle released the July 2021 Critical Patch Update (CPU), which fixed 342 vulnerabilities of varying risk levels. This CPU involves multiple commonly used products, such as Oracle Database Server, Oracle Java SE, Oracle Fusion Middleware, Oracle MySQL, and Oracle Communications. Oracle strongly...
Microsoft’s July 2021 Security Updates Fix Multiple Products’ High-Risk Vulnerabilities
Overview According to NSFOCUS CERT's monitoring, Microsoft released July 2021 Security Updates on July 14 to fix 117 vulnerabilities, including high-risk remote code execution and privilege escalation, in widely used products like Windows, Microsoft Office, Microsoft Edge, Visual Studio, and SharePoint Server. In the vulnerabilities fixed by this month's security...
SolarWinds Serv-U Remote Code Execution Vulnerability (CVE-2021-35211) Threat Alert
Overview Recently, NSFOCUS CERT, through ongoing monitoring, found that SolarWinds released a security advisory fixing a remote code execution vulnerability (CVE-2021-35211). Microsoft reported to SolarWinds that they had discovered that the vulnerability was exploited in the wild and provided a proof of concept of the exploit. Unauthenticated, remote attackers could...
Windows Print Spooler RCE Vulnerabilities (CVE-2021-1675/CVE-2021-34527) Mitigation Guide
Overview On July 7, 2021, Beijing time, Microsoft released a security patch on the PrintNightmare vulnerability (CVE-2021-34527). NSFOCUS CERT recommends that users install this patch as soon as possible. On June 29, NSFOCUS CERT found that a security researcher published an exploit of the Windows Print Spooler remote code execution...
“Netfilter” malicious driver bypasses Microsoft’s signature system
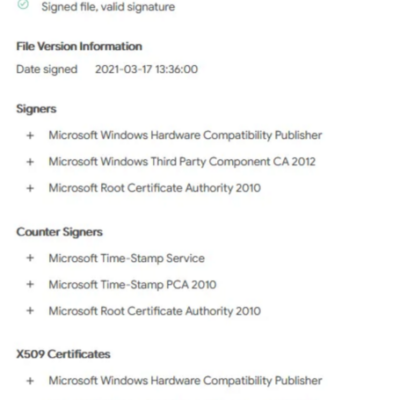
In June 2021, German computer security solutions software company G Data Software detected a malicious driver named "Netfilter". Unexpectedly, the malicious driver bypassed and obtained Microsoft's file signature. When Microsoft learned about it, it immediately added the signature of the malware to the security center of the Windows system for...