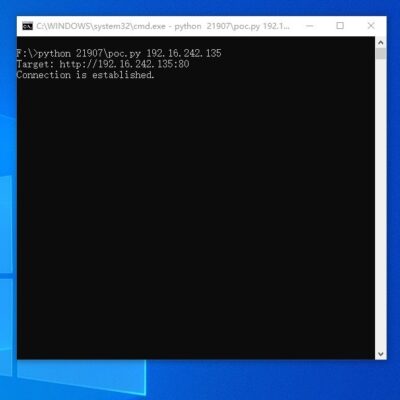
Overview On January 12, NSFOCUS CERT detected that Microsoft released a monthly security update, which fixed an HTTP protocol stack remote code execution vulnerability (CVE-2022-21907). A buffer overflow can occur due to a boundary error in the HTTP Trailer Support feature in the HTTP stack (HTTP.sys). An unauthenticated attacker can...

Category: Emergency Response
Apache log4j Deserialization and SQL Injection Vulnerability (CVE-2022-23302/CVE-2022-23305/CVE-2022-23307) Alert
Overview On January 19, NSFOCUS CERT detected that Apache released a security bulletin that disclosed three Log4j vulnerabilities, all of which affected the Apache Log4j 1.x version, and the official support and maintenance are no longer available. Please take measures as soon as possible to protect the relevant users. Apache...
Oracle January Critical Patch Update for All Product Families
Overview On January 19, 2022, NSFOCUS CERT monitoring found that Oracle officially released the CPU (Critical Patch Update) in January. A total of 497 vulnerabilities of varying degrees were fixed this time. This security update involves Oracle WebLogic Server. , Oracle MySQL, Oracle Java SE, Oracle FusionMiddleware, Oracle Retail Applications...
Apache Dubbo Remote Code Execution Vulnerability (CVE-2021-43297) Notification
Overview On January 12, NSFOCUS CERT found that Apache issued a security notice to fix a remote code execution vulnerability (CVE-2021-43297) in Dubbo. Due to a deserialization vulnerability in Dubbo's hessian-lite, an unauthenticated attacker could exploit the vulnerability to remotely execute arbitrary code on the target system. Most Dubbo users...
3 Steps to Mitigate the Log4j2 Vulnerabilities Using NSFOCUS WAF
On December 9, NSFOCUS monitored the disclosure of the Apache Log4j2 remote code execution vulnerability (CVE-2021-44228) on the Internet. Apache Log4j2 is an open source Java logging framework, which is widely used in middleware, development frameworks and web applications to record log information. The vulnerability PoC has been made public...
ApacheLog4j Remote Code Execution Vulnerability (CVE-2021-44228, CVE-2021-45046, CVE-2021-45105) Threat Alert updated on Dec 20 2021
Overview The update involves (CVE-2021-45046) and (CVE-2021-45105) vulnerability information, scope of influence, product rules, official version and workaround. On December 9 2021, NSFOCUS CRET has detected the disclosure of Apachelog4j Remote Code Execution Vulnerability (CVE-2021-44228). Due to the recursive parsing of some functions of apachelog4j2, unauthenticated attackers can execute arbitrary...