I. Abstract NSFOCUS Security Labs recently discovered a new attack process based on phishing documents in their daily threat-hunting operations. Delving deeper into this finding through extensive research, they confirmed two new Trojan horse programs and many rare attack techniques and tactics. NSFOCUS Security Labs believes that this new attack...
Autor: NSFOCUS
Apple Multiple Product Security Vulnerabilities Notification
Overview Recently, NSFOCUS CERT has detected that Apple has officially fixed three zero-day exploit in multiple products. These vulnerabilities exist in the wild. Affected users should take protective measures as soon as possible. The details of the vulnerability are as follows: Apple WebKit Arbitrary Code Execution Vulnerability (CVS 2023-41993): There...
Unlocking the Future of Cybersecurity: Meet Us at GovWare 2023
Today's ever-evolving digital landscape presents unparalleled opportunities alongside formidable cybersecurity challenges, making the security of organizations' networks and applications more crucial. As a global network and cyber security leader, we're excited to invite you to join us at GovWare 2023, a pivotal event held at the Sands Expo and Convention...
GitLab Unauthorized Call Vulnerability (CVC-2023-5009) Notification
Overview Recently, NSFOCUS CERT monitored that GitLab officially issued a security notice, and fixed an unauthorized call vulnerability in GitLab Enterprise Edition (EE). The vulnerability is a bypass of CVE-2023-3932. An attacker with low privileges can abuse the scan execution policy to run pipelines without the user's consent. Successful exploitation...
Feature Adaptations on Slave ADSM in a High Availability Environment
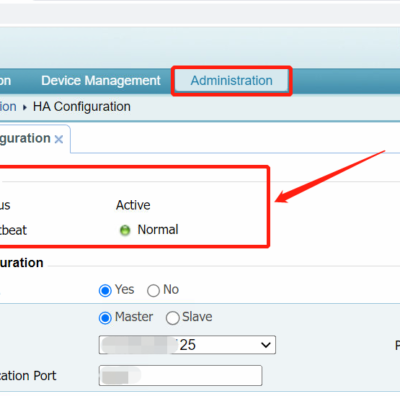
Sometimes, to ensure continuous business operations in the event of equipment failure, it is a common practice to configure High Availability (HA) using two ADSM devices. You can configure High Availability (HA) in ADSM by navigating to Administration > Local Settings > HA Configuration. Master: Slave: The master handles all...
Adobe Acrobat and Reader Arbitrary Code Execution Vulnerability (CVE-2023-26369) Notification
Overview Recently, NSFOCUS CERT monitored Adobe's official security announcement and fixed an arbitrary code execution vulnerability (CVE-2023-26369). Due to a cross-border write flaw, an unauthenticated attacker could finally execute arbitrary code on the target system by exploiting this vulnerability. This vulnerability is being exploited in the wild. Affected users should...