Vulnerability Overview Recently, NSFOCUS CERT detected that the security community disclosed a supply chain backdoor vulnerability in XZ-Utils (CVE-2024-3094), with a CVSS score of 10. Since the underlying layer of SSH relies on liblzma, when certain conditions are met, an attacker can use this vulnerability to bypass SSH authentication and...
Autor: NSFOCUS
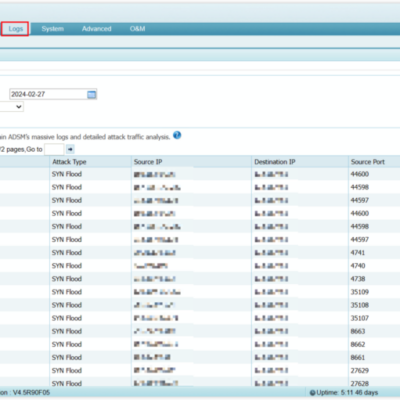
Policy Adjustment Based on Attack Events in ADS
This article provides a brief explanation of policy fine-tuning in ADS. Please note that fine-tuning the protection policy is a time-consuming process. This article focuses on how to check attack details in ADS based on attack events and optimize policies accordingly. Due to different versions of ADS, the screenshots shown...
JumpServer Remote Code Execution Vulnerability (CVE-2024-29201/CVE-2024-29202) Notice
Overview Recently, NSFOCUS CERT detected that JumpServer issued a security announcement and fixed two remote code execution vulnerabilities. At present, the PoC of the vulnerability has been made public. Affected users should take protective measures as soon as possible. CVE-2024-29201: Since the Ansible module in JumpServer does not perform complete...
Modern DDoS Attacks and the Rise of DDoS Coalitions
DDoS attacks have become an indispensable weapon to paralyze network systems in cyber warfare. Emerging DDoS attacks, such as HTTP/2 Rapid Reset and SLP reflection amplification attacks, are constantly emerging. Both attackers and defenders are struggling to upgrade their technology in order to discover new offensive and defensive strategies. DDoS...
XZ Utils Backdoor Vulnerability (CVE-2024-3094) Advisory
Overview NSFOCUS CERT recently detected that a backdoor vulnerability in XZ Utils (CVE-2024-3094) was disclosed from the security community, with a CVSS score of 10. Because the SSH underlying layer relies on liblzma, an attacker could exploit this vulnerability to bypass SSH authentication and gain unauthorized access to affected systems,...
Linux Kernel Privilege Escalation Vulnerability (CVE-2024-1086) Alert
NSFOCUS CERT has detected that details and a proof-of-concept (PoC) tool for a Linux kernel privilege escalation vulnerability CVE-2024-1086, have been publicly disclosed recently. Due to a use-after-free vulnerability in the netfilter: nf_tables component of the Linux kernel, the nft_verdict_init() function allows the use of positive values as a drop...